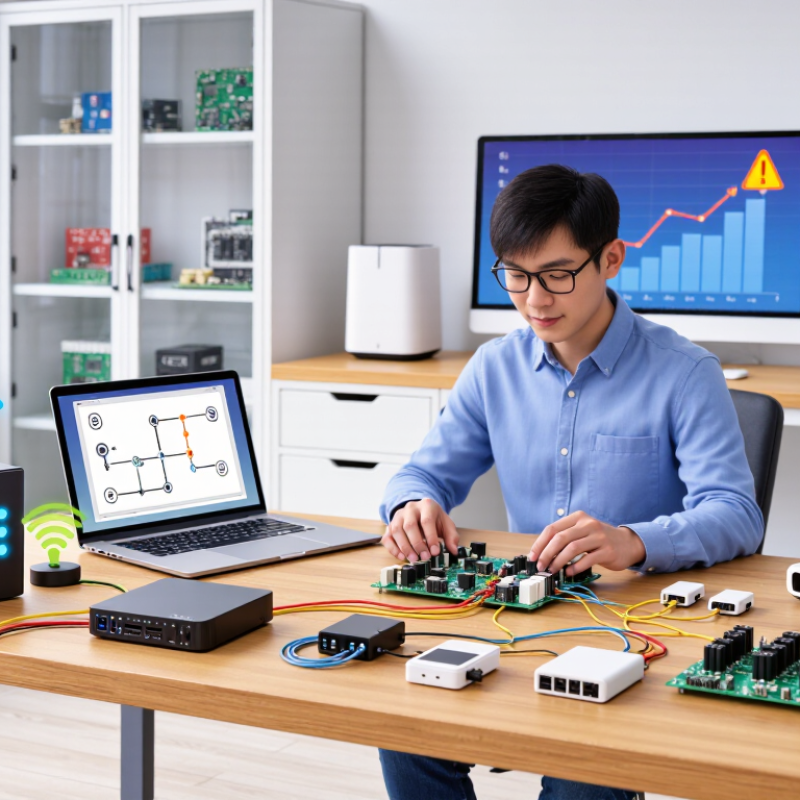
Choosing the top ten IoT trainers requires more than polished lessons or impressive completion numbers. The useful test is security coverage. Trainers should map each module to NISTIR 8259, including device identity, secure updates, data protection, and vulnerability handling. They should explain ETSI EN 303 645 controls in practical language. Learners must know what to configure, inspect, and document. Not just memorize clauses. Good programs use a sensor, gateway, and dashboard. Learners change credentials, disable unused services, and review failed update logs.
A credible evaluation checks experience with threat modeling, embedded systems, cloud interfaces, and incident response. It examines assessment quality, not marketing claims. Strong trainers provide lab evidence, versioned exercises, and clear references to both standards. They should discuss secure defaults, data minimization, resilience, and vulnerability disclosure. Short quizzes help, but practical reviews matter more. Ask learners to produce a device inventory, security risk record, update plan, and recovery test. Another reviewer should be able to repeat the work.
Some courses look complete yet skip physical access attacks or insecure interfaces. That gap matters. A realistic review may also uncover certificate rotation errors after learners pass the final test. The scoring model should expose these weaknesses. Standards evolve, and training material can age quietly. Trainers need review schedules, transparent change notes, and honest limits. During evaluation, record the firmware version, test date, failed control, and corrective action.